I spent two hours on enabling some distributed transaction between my iis server and windows 2003 server running sql server 2005. Thanks to people on the net , I compiled the following links.
For enabling DTC:
http://forums.microsoft.com/MSDN/ShowPost.aspx?PostID=230390&SiteID=1
http://blogs.msdn.com/florinlazar/archive/2004/06/18/159127.aspx
Followed the instructions both on IIS server and Sql server boxes.
Dont forget to enable both firewalls for msdtc and sqlserver!
here is what they say:
First verify the "Distribute Transaction Coordinator" Service isrunning on both database server computer and client computers
1. Go to "Administrative Tools > Services"
2. Turn on the "Distribute Transaction Coordinator" Service if it is not runningIf it is running and client application is not on the same computer asthe database server, on the computer running database server1. Go to "Administrative Tools > Component Services"
3. On the left navigation tree, go to "Component Services > Computers> My Computer" (you may need to double click and wait as some nodesneed time to expand)
4. Right click on "My Computer", select "Properties"
5. Select "MSDTC" tab
6. Click "Security Configuration"
7. Make sure you check "Network DTC Access", "Allow Remote Client","Allow Inbound/Outbound", "Enable TIP" (Some option may not benecessary, have a try to get your configuration)
8. The service will restart
9. BUT YOU MAY NEED TO REBOOT YOUR SERVER IF IT STILL DOESN'T WORK(This is the thing drove me crazy before)On your client computer use the same above procedure to open the"Security Configuration" setting, make sure you check "Network DTCAccess", "Allow Inbound/Outbound" option, restart service and computerif necessary.On you SQL server service manager, click "Service" dropdown, select"Distribute Transaction Coordinator", it should be also running onyour server computer.
On client and server:
netsh firewall set allowedprogram %windir%\system32\msdtc.exe MSDTC enable

May 28, 2006
CMS Logbook 5 - Setting default role for anonymous users (part 2)
First of all, this is valid for asp.net only.
Here's the situation, I have some business logic that needs authorization. Yet the not logged in users should have some access defined with the role 'anonusers'. The problem is how the business logic (a seperate class library) gets the authentication info. As this is a web site with Forms Authentication I used HttpContext.Current field to get the authenticated user.
The business logic , uses a base class property namely CurrentUser to get the current user authenticated:
public IPrincipal CurrentUser
{
get
{
if (HttpContext.Current !=
null)
return HttpContext.Current.User;
else
{
GenericIdentity
defaultIdentity = new GenericIdentity("anonymous");
string[] roles = new
string[1];
roles[0] = "anonusers";
GenericPrincipal genericPrincipal
=
new GenericPrincipal(defaultIdentity, roles);
return
genericPrincipal;
}
}
}
As you see if there is no user found in the context, this returns a 'anonymous' principal.
By this way I can now unit test all the business logic.
Ankara'da Seracilik
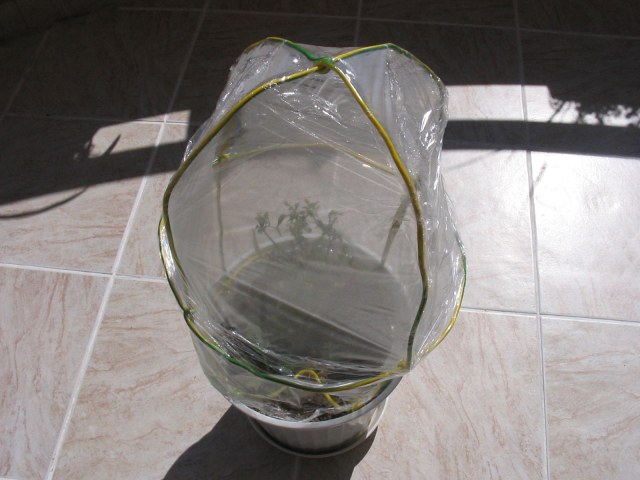
Finike ve Antalya'nin seraciliktaki basarisini takiben ben de neden Ankara'da da seracilik yapmayalim dedim. Degerli belediye baskanimiz Melih Gokcek 'in Ankara'da gol ve musluk sayisini arttirmadaki azmi de bana ayrica bir guc verdi. Ben de ilk seracilik projemi balkonda gerceklestirdim.
Gerekli malzemeler:
Kalin tel
Mutfaklarda yiyecek sarmak icin kullandigimiz seffaf poset
Yapilis:
Teli bukerek bir sekil olusturun , icine saksiyi alabilecek kadar buyuk olsun, daha sonra seffaf ambalajla kaplayin .
Bakalim icerdeki cin biberi bu giysiyi nasil karsilayacak?
April 11, 2006
CMS Logbook 4 - Setting default role for anonymous users
For anonymous users, I had to define a default role. Thus I would have fine grained control on what they can do in the cms site without declaring a Deny All grant. The first solution for such a thing is defining a default formsauthentication ticket for every anonymous request , that is speaking for ASP.NET 2.0 global.asax file ;
This works but not a neat solution. I could not find a better solution on a built-in role definition for anon users so I have taken the following approach. In my CMS system all authorization requests are handled from a single business class , so I have changed it accordingly to define a default role for anon users, that is something like;void Application_AuthenticateRequest(Object sender, EventArgs e)
);
{
HttpApplication app = (HttpApplication)sender;
if (!app.Request.IsAuthenticated && app.Context.User == null)
{
FormsIdentity identity = new FormsIdentity(new
FormsAuthenticationTicket("anonymous", true, 5));
string role = "anonusers";
app.Context.User = new GenericPrincipal(identity,
new string[] { role }
}
}
public
Authorizer():base()
{
SetupRoles(base.CurrentUser.Identity.Name);
}
public Authorizer(User user) : this(user.UserName)
{
}
public Authorizer(string username) : base()
{
SetupRoles(username);
}
private void SetupRoles(string username)
{
if (String.IsNullOrEmpty(username))
username = base.AnonymousUserName;
userroles = FindRolesOfUser(username);
}
March 30, 2006
CMS Logbook 3: Users and multiple roles in an application
In an application, when users are member of more than one roles some complications arise. This can be like;
- What is the user's default role when logged in? For example if the application customizes the user interface according to role, then what role will be picked up?
- If a user has some authorization grant for a role and a deny for another which will be taken into acccount?
For the question 1 , I think that a default role should be given for every user, and this should be used for view customization. For an ASP.NET 2.o application this could be stored in user profile.
For the question 2, I plan to take this approach, If user has at least one grant for an operation then it is sufficient for the authorization.
March 20, 2006
CMS Logbook 2 : Data from different angles
I have been working on a simple content management system for more than a month now and things are getting more interesting for me lately. What makes my simple content management system?(cms from now on).
- Content is tree based.
- Leaves can be containers or the content itself.
- There are different kind of contents.
- Some contents are approvable some are not.
- There is an authorization system based on ASP.NET 2.0 Membership and Role Providers.
- The authorization system is fine grained till the leaves.
- The authorization system relies on user roles rather than individual users.
- The authorization system consists of access rights as view, edit, delete, create new and list.
- List stands for if the user has rights to list the children nodes of the node.
- View stands for if the user has rights to view the content on the node.
- Delete stands for if the has right to delete the node.(this operation undergoes a check for finding references for the content on the node)
- Create New stands for if the user has right to add a new node to the current node. A new node will be automatically editable and deletable for the adding user.
- Edit stands for if the user has right to edit the content on the node
Subscribe to:
Posts (Atom)